Key Statistics Summary
- The Australian Signals Directorate (ASD) received more than 94,000 cybercrime reports in FY2022-23, equivalent to one report roughly every six minutes, according to the ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au).
- The average self-reported cost of cybercrime was $46,000 per report for small businesses, $97,200 for medium businesses and $71,600 for large businesses, according to the same ASD report.
- The global average cost of a data breach reached USD $4.45 million in 2023, with the Australian average sitting at AUD $4.26 million, according to IBM Security's Cost of a Data Breach Report (ibm.com/reports/data-breach).
- Australians reported losing $2.74 billion to scams in 2023, a decrease from the record $3.1 billion lost in 2022, according to the ACCC's Targeting Scams report and the National Anti-Scam Centre (accc.gov.au).
- Health service providers have consistently ranked among the most reported sectors for data breach notifications, according to the Office of the Australian Information Commissioner's (OAIC) Notifiable Data Breaches Report (oaic.gov.au).
- Human error and social engineering remain leading contributors to breaches worldwide, according to Verizon's Data Breach Investigations Report (verizon.com/business/resources/reports/dbir).
Introduction
Australian organisations of every size now operate in an environment where cyber risk is a standing item on the agenda, not an occasional concern. Boards, school councils, government teams and small business owners are all being asked to make decisions about security spending, incident response and staff training, often without a clear picture of what "normal" looks like. This article brings together the publicly available data from Australian Government agencies, international research bodies and industry analysts to give practitioners a single, citable reference point.
This resource is written for IT managers, business owners, compliance leads and anyone briefing a board or council on cyber risk. It does not rank threats by how frightening they sound. In line with the view that organisations deserve to be safe, not scared, the figures below are presented in plain terms so readers can weigh actual likelihood and cost against their own risk appetite, rather than react to headlines. Every statistic is attributed to its original source so it can be checked and cited further.
Free, 45 minutes
Not sure where your school or business stands?
Book a free IT health check. We look at your environment, rank the risks in plain English and tell you what deserves attention first. No jargon, no hard sell.
Incidence and Threat Volume Statistics
- The ASD's ReportCyber portal received over 94,000 cybercrime reports in the 2022-23 financial year, an average of one report every six minutes, according to the ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au).
- Business email compromise remained one of the costliest cybercrime types reported to ASD, with attackers frequently impersonating suppliers or executives to redirect payments, according to the same report.
- Ransomware continues to be assessed by the ASD as one of the most destructive cyber threats facing Australian organisations, given its capacity to disrupt operations across an entire network rather than a single system.
- Globally, the Verizon Data Breach Investigations Report found that the human element, including phishing, stolen credentials and simple error, was a factor in the large majority of breaches analysed (verizon.com/business/resources/reports/dbir).
- The Australian Government has continued to expand ReportCyber and the Cyber Security Act reporting settings, reflecting an assessment that a meaningful share of incidents affecting Australian businesses still go unreported to authorities.
No single agency captures every incident that occurs across the Australian economy, since reporting is voluntary for most organisations outside regulated sectors. The volume figures above should be read as a floor, not a ceiling, on actual incident levels.
Average Self-Reported Cost of Cybercrime by Business Size
| Business size | Average cost per cybercrime report | Source |
|---|---|---|
| Small business | $46,000 | ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au) |
| Medium business | $97,200 | ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au) |
| Large business | $71,600 | ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au) |
The fact that medium-sized businesses reported a higher average cost than large businesses is notable. Large organisations typically carry more mature detection and response capability, which can contain an incident before it escalates, while medium businesses often carry meaningful digital footprints without the security budget of an enterprise.
Cost of Cybercrime and Data Breaches
- The global average cost of a data breach was USD $4.45 million in 2023, according to IBM Security's Cost of a Data Breach Report, produced with the Ponemon Institute (ibm.com/reports/data-breach).
- The average cost of a data breach for organisations operating in Australia was AUD $4.26 million, according to the same IBM report.
- Costs associated with a breach typically extend well beyond the immediate incident, including detection, notification, lost business and post-breach response, per IBM's methodology.
- Organisations that contained a breach faster generally reported lower overall costs, according to IBM's analysis of breach lifecycle length across the dataset.
- The ACCC's Targeting Scams report recorded $2.74 billion in reported scam losses across Australia in 2023, down from $3.1 billion in 2022, the first year-on-year fall in several years (accc.gov.au).
Average Cost of a Data Breach: Australia vs Global
| Metric | Global average | Australian average | Source |
|---|---|---|---|
| Average total cost of a data breach (2023) | USD $4.45 million | AUD $4.26 million | IBM Security, Cost of a Data Breach Report (ibm.com/reports/data-breach) |
Reported Scam Losses in Australia, Year on Year
| Year | Reported scam losses (AUD) | Source |
|---|---|---|
| 2021 | Over $2 billion | ACCC Targeting Scams Report (accc.gov.au) |
| 2022 | $3.1 billion | ACCC Targeting Scams Report (accc.gov.au) |
| 2023 | $2.74 billion | ACCC / National Anti-Scam Centre (accc.gov.au) |
The 2023 decline followed increased action from banks, telecommunications providers and digital platforms under the National Anti-Scam Centre model, according to the ACCC. It is the first recorded drop after several years of consistent growth in reported losses.
Industry and Sector Impact
The OAIC's Notifiable Data Breaches Report, published twice yearly, tracks which sectors report breaches under the Notifiable Data Breaches scheme. Across multiple reporting periods, health service providers have consistently ranked as the most frequently reporting sector, followed closely by the finance sector, according to OAIC (oaic.gov.au). Legal, accounting and management services, along with the education sector, have also appeared regularly in the top reporting categories.
A genuinely cited table of sector-by-sector breach percentages is not included here, since exact figures shift between each six-monthly OAIC report and a stale percentage would misrepresent the current position. Readers who need the current period's exact sector breakdown should consult the latest OAIC Notifiable Data Breaches Report directly.
- Health service providers have been the most reported sector under the Notifiable Data Breaches scheme in the majority of reporting periods since the scheme began, according to OAIC.
- Malicious or criminal attacks, rather than human error, have been the leading cause of reported data breaches in most OAIC reporting periods, though human error remains a substantial secondary cause.
- Government agencies, education providers and not-for-profits have all featured in OAIC's reported breach data, reflecting the breadth of sectors now holding sensitive personal information.
- According to IBISWorld Australia, demand for cyber security services has grown as businesses across sectors increase spending on threat detection, compliance and managed security functions (ibisworld.com).
SME Cyber Security Vulnerabilities
Small and medium businesses make up the large majority of Australian businesses registered with the Australian Bureau of Statistics, and they typically operate with far less dedicated security capability than an enterprise. This gap between exposure and capability is the recurring theme in SME-focused cyber security data.
- Small businesses reported an average cybercrime cost of $46,000 per incident, a figure that can represent a material share of annual revenue for a business of that size, according to the ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au).
- The ASD's guidance for small business specifically highlights multi-factor authentication, regular backups and prompt software updates as the highest-value controls, reflecting the reality that SMEs cannot implement every control available to an enterprise (cyber.gov.au).
- Business email compromise and invoice fraud are frequently reported by smaller businesses, since attackers can automate these approaches at scale across many targets rather than needing to customise an attack per organisation.
- According to the ABS, small businesses represent the overwhelming majority of actively trading businesses in Australia, meaning that even a modest per-business risk translates into a very large aggregate exposure across the economy (abs.gov.au).
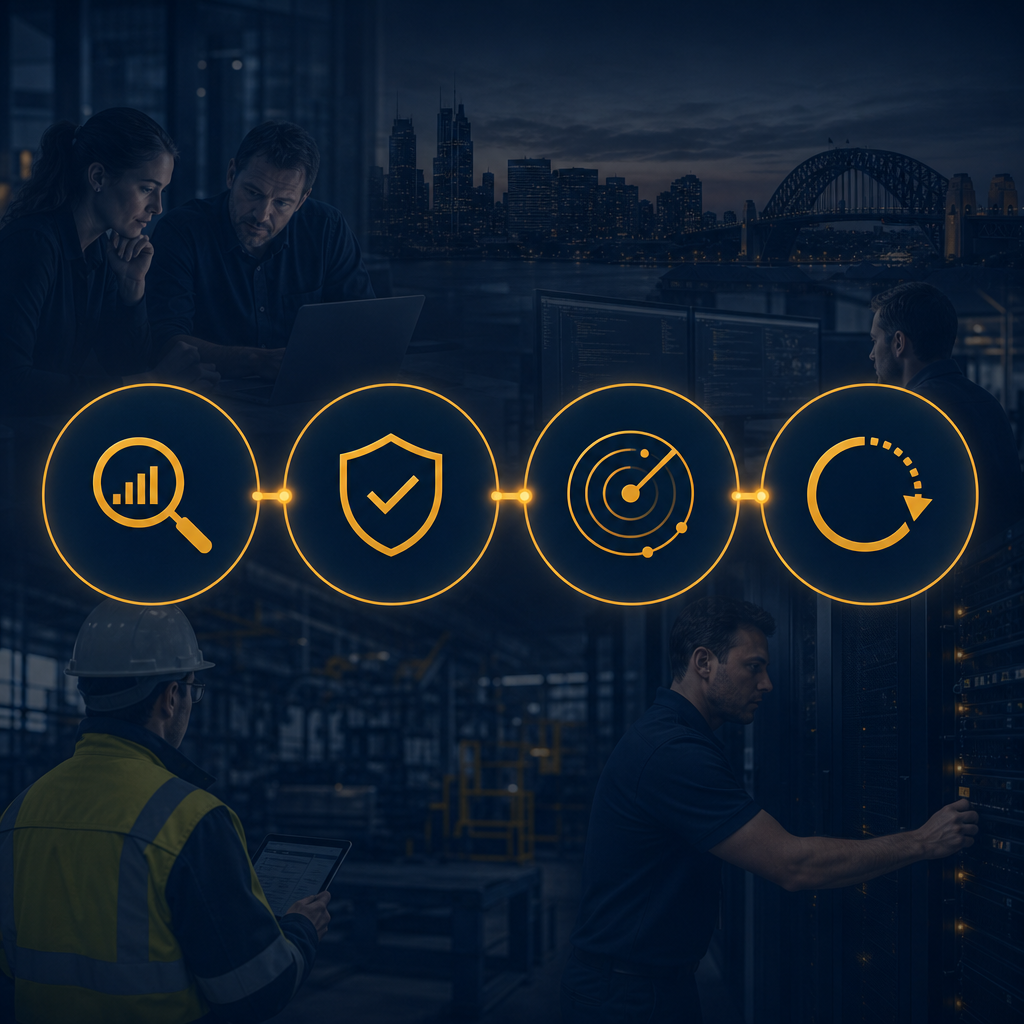
A cyber security program built around assessing risk first, protecting the highest-value systems, detecting incidents early and having a tested recovery plan tends to close most of this gap without requiring enterprise-level budgets. This sequence, sometimes summarised as Assess, Protect, Detect, Recover, reflects the order in which most practical improvements should happen rather than a menu to be picked from at random. More detail on this approach is available at SCCS's cyber security page.
Australian Market Statistics
- The ASD received over 94,000 cybercrime reports in FY2022-23, an average of one every six minutes, according to the ASD Annual Cyber Threat Report 2022-23 (cyber.gov.au).
- Average self-reported cybercrime costs ranged from $46,000 (small business) to $97,200 (medium business) per incident, according to the same report.
- Australians lost $2.74 billion to scams in 2023, according to the ACCC and National Anti-Scam Centre (accc.gov.au).
- Health service providers have remained the most frequently reported sector under the Notifiable Data Breaches scheme, according to OAIC (oaic.gov.au).
- The Australian cyber security services industry has grown as businesses lift spending on managed detection, compliance and incident response, according to IBISWorld Australia (ibisworld.com).
- The ABS notes that small businesses make up the vast majority of actively trading businesses in Australia, underscoring why SME-focused controls carry national significance (abs.gov.au).
Australia's regulatory settings continue to shift in response to this data. Mandatory reporting obligations under the Notifiable Data Breaches scheme, combined with sector-specific requirements for critical infrastructure, mean that more Australian organisations are required to formally record and report incidents than in previous years. This has improved the visibility of the data summarised here, even though under-reporting outside regulated sectors remains a known limitation.
What This Looks Like in Practice
Statistics describe the pattern across the economy, but the practical impact shows up at the level of a single organisation. Two examples from direct field experience illustrate how the categories above translate into day-to-day decisions.
An independent school needed its network, cyber security and daily IT support handled as one coordinated function rather than as separate contracts. Once that responsibility was taken on end to end, staff were able to return to teaching instead of troubleshooting. In a school environment, the standard worth applying to any technology decision is simple: if technology steals a minute of the lesson, it has failed. That test applies just as much to a patch that breaks a login as it does to a phishing email that reaches a teacher's inbox.
Separately, ageing device fleets create a cyber security exposure of their own, since old devices holding client and student data are a genuine risk if retired carelessly. Through the PonyUp for Good partnership, retired devices have their data destroyed, are refurbished and resold, with half the profits converted into meals. That partnership has funded more than 150,000 meals and diverted more than 40 tonnes of technology from landfill. It is a reminder that end-of-life device handling belongs inside a cyber security program, not outside it.
Key Takeaways
- Treat cyber security as four disciplines working together in order: Assess, Protect, Detect, Recover. Skipping the assessment step is the most common reason organisations over-invest in tools that do not match their actual risk.
- SME-scale businesses face a materially different cost profile to large enterprises. The controls that matter most, multi-factor authentication, backups and patching, are the same ones ASD recommends as the highest-value starting point.
- Sector matters. Health, finance and government-adjacent organisations should expect closer regulatory scrutiny and should benchmark themselves against OAIC's sector-specific breach data rather than economy-wide averages.
- Device retirement is a security event, not just an asset management task. Data destruction should be verified, not assumed.
- These figures are a starting point for a conversation with a board, council or leadership team, not a substitute for an assessment of a specific environment. Organisations that want a plain-language reading of what these benchmarks mean for their own risk position can arrange a conversation via SCCS's contact page or book a time directly. Ongoing management of the controls discussed above, including patching, backup and monitoring, sits within SCCS's managed services.
Methodology and Disclaimer
Statistics sourced from publicly available research and industry reports, including Australian Government agencies (ASD, OAIC, ABS, ACCC), international industry research (IBM Security, Verizon) and industry analysts (IBISWorld). Figures are drawn from the most recently published editions of each source available at the time of writing and are attributed to the specific report and year in which they were published. Where a data point could not be tied to a real, named source, it has been omitted rather than estimated. Readers should verify individual figures against the original source before publishing or relying on them, since some reports (notably OAIC's Notifiable Data Breaches Report) are updated on a six-monthly cycle and figures can change between editions.
Sources
- Australian Signals Directorate, Annual Cyber Threat Report 2022-23 (https://www.cyber.gov.au)
- Office of the Australian Information Commissioner, Notifiable Data Breaches Report (https://www.oaic.gov.au/privacy/notifiable-data-breaches/notifiable-data-breaches-publications)
- Australian Competition and Consumer Commission, Targeting Scams Report (https://www.accc.gov.au)
- Scamwatch / National Anti-Scam Centre (https://www.scamwatch.gov.au)
- IBM Security, Cost of a Data Breach Report (https://www.ibm.com/reports/data-breach)
- Australian Bureau of Statistics (https://www.abs.gov.au)
- IBISWorld Australia, Cyber Security Services in Australia (https://www.ibisworld.com/au/)
- Verizon, Data Breach Investigations Report (https://www.verizon.com/business/resources/reports/dbir/)
- Australian Cyber Security Centre small business guidance, hosted by the Australian Signals Directorate (https://www.cyber.gov.au)
- Australian Signals Directorate (https://www.asd.gov.au)
Free download
The School IT & Cyber Readiness Checklist
Twelve points, ten minutes with a highlighter, and you know exactly what to fix first.
Frequently asked questions
What is the most reliable source for Australian cybersecurity statistics?
The Australian Signals Directorate's Annual Cyber Threat Report and the OAIC's Notifiable Data Breaches Report are the two most consistently cited government sources, since both are published on a regular schedule and cover different parts of the picture: overall cybercrime volume and cost (ASD) versus formally notified data breaches (OAIC).
How much does cybercrime typically cost a small Australian business?
According to the ASD Annual Cyber Threat Report 2022-23, the average self-reported cost of cybercrime for a small business was $46,000 per report. This figure covers direct costs and does not always capture indirect impacts such as lost customers or reputational damage.
Which industries are most affected by data breaches in Australia?
Health service providers and the finance sector have consistently ranked among the most frequently reporting sectors under the OAIC's Notifiable Data Breaches scheme. Government, legal, education and not-for-profit organisations have also featured regularly.
Is cybercrime increasing or decreasing in Australia?
Reported cybercrime volumes to the ASD's ReportCyber portal have generally trended upward over recent years, while reported scam losses tracked by the ACCC fell in 2023 for the first time in several years. The two data sets measure different things, so they should not be read as contradictory.
Do these statistics apply equally to small businesses and large enterprises?
No. Cost per incident, the type of threat most commonly encountered and the maturity of available controls differ significantly by organisation size. SME-specific figures, such as ASD's small business cost data, are a more useful benchmark for smaller organisations than economy-wide averages.
What should an Australian business do with these statistics?
Use them to inform, not replace, a proper risk assessment. Benchmarks are most useful for framing a conversation with a board or leadership team about where an organisation sits relative to its sector, and for prioritising the highest-value controls first, such as multi-factor authentication, backups and patching.
Ian Pearce
General Manager, Sales and Services at Southern Cross Computer Systems